Make code compliance part of everyday development
Seamlessly bring compliance into traditional and agentic workflows, and demonstrate it at scale with automated standards enforcement and code-level evidence.


Why is code compliance difficult to scale?
Meeting compliance requirements like PCI DSS, STIG, SOC 2, DORA, CRA, or HIPAA is a high-stakes, non-negotiable requirement for many organizations. Yet proving compliance at the code level is often a manual, time-consuming, and error-prone process for developers.

Standards enforcement
Compliance standards can be applied inconsistently across traditional and agentic workflows.

Fragmented audit evidence
Manually gathering evidence for audits is a painful, disruptive fire drill that pulls teams away from innovation.

Business risk
Non-compliance can lead to significant financial penalties, reputational damage, and loss of business.

Late discovery of issues
Finding compliance gaps late in development cycles requires significant rework and can delay critical releases.
SonarQube automates your path to provable code compliance
SonarQube embeds compliance-relevant controls into development workflows, helping teams enforce secure coding standards, gain control over dependencies, catch risks before release, and generate code-level evidence as they build. This provides a scalable code verification and governance layer across traditional and agentic development.
Centralized criteria management
Enforce your specific security, maintainability and reliability rules consistently for every developer and every AI agent.
Automatic audit trail
Generate a trail for all code issues found, providing a clear record of detection and remediation.
Streamlined reporting
Easily prove that code from both developers and AI agents complies with regulatory and industry standards.
"We have used SonarQube since very early on and it is incalculable to define the importance of pointing at the solution in response to questions from audits and regulators!"
Gary Barter
Executive Director
Key capabilities for regulatory compliance and reporting
Built-in reports
Streamlined compliance reporting, aligned with OWASP Top 10, OWASP ASVS, CRA, PCI DSS, CWE Top 25, STIG, CASA, WCAG, etc.
MISRA C++:2023
100% coverage of all 179 MISRA C++:2023 guidelines in SonarQube
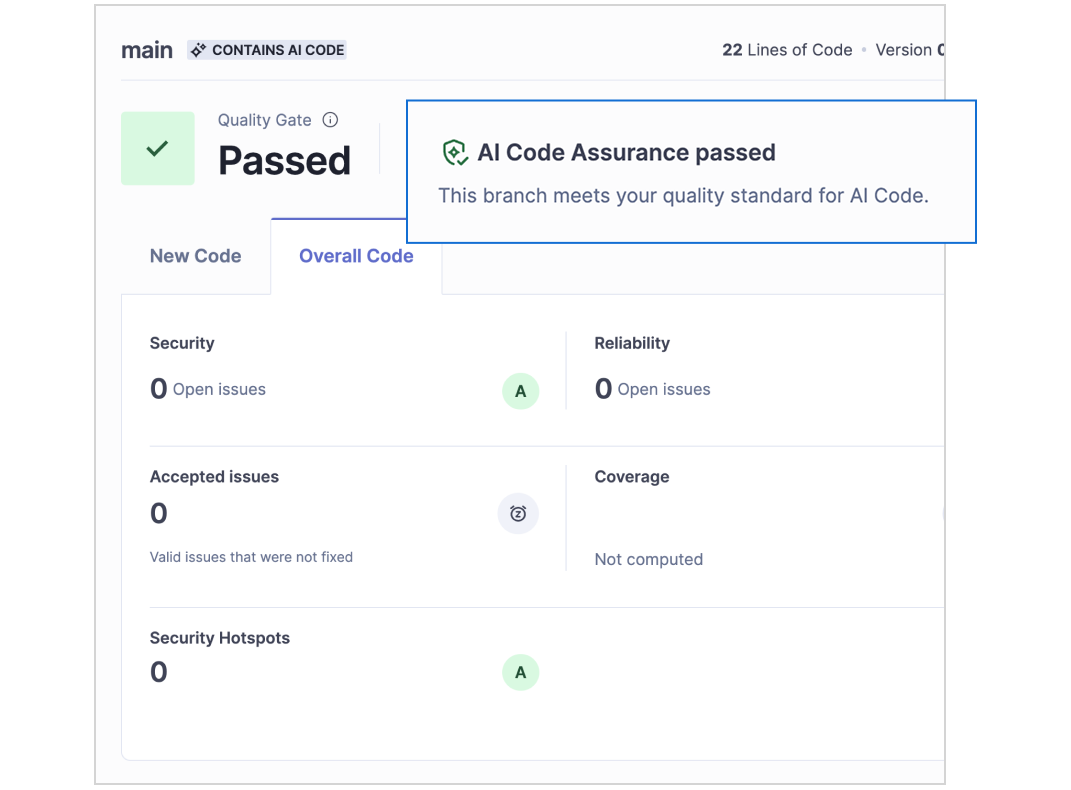
AI Code Assurance
Helps govern AI-powered development by independently verifying AI code against consistent code quality and security standards in agentic workflows, without slowing agents down
Centralized management
Ensures all developers and agents work with the same set of compliance rules, directly in the IDE and across agentic workflows
Automatic code review
Analysis results displayed directly in every pull request and branch, preventing non-compliant code from being merged
Customizable quality profiles and gates
Automatically blocks pull requests and branches that don't meet your required quality, security, or test coverage standards
Software Composition Analysis (SCA)
Identify vulnerable direct and transitive dependencies, assess reachability and license risk, and generate SBOMs (available with SonarQube Advanced Security)
Ticketing integration
Push compliance issues directly to tickets for seamless tracking and remediation
Operationalize compliance without disrupting software delivery
Four products that embed compliance-relevant controls into AI coding workflows, from standards-aware generation through independent verification, security assurance, and remediation.
Sonar Vortex
Brings compliance-relevant guidance, governance and verification into the agentic development loops, helping agents follow organizational standards and constraints before changes reach review.
- Relevant context — Uses existing SonarQube analysis to give agents coding standards, architecture, and dependency context beyond the current file.
- In-workflow governance — Applies existing quality profiles across supported agentic tools, reducing duplicated policies and inconsistent controls.
- Multilayered verification — Vortex analyzes changes as agents work, while SonarQube independently verifies them in pull requests and CI before merge.
SonarQube Advanced Security
Identify vulnerabilities, dependency risks, exposed secrets, and insecure configurations before release, with findings captured for remediation and compliance reporting.
- Advanced SAST across application and dependency code: Traces data flows through open-source libraries to uncover vulnerabilities that conventional analysis may miss.
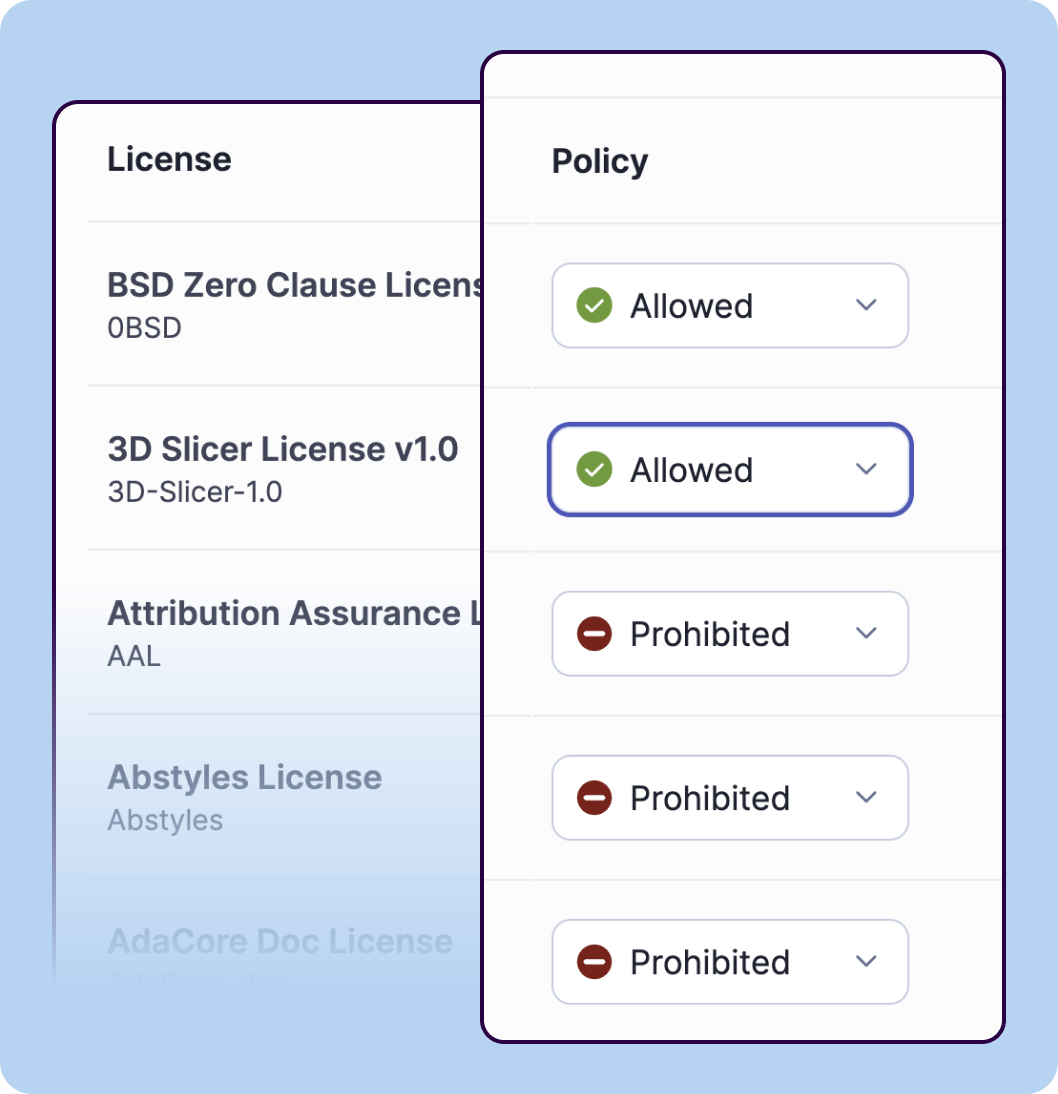
- SCA and component governance: Identifies vulnerable or malicious direct and transitive dependencies, assesses reachability and license risk, and generates SBOMs and VEX.
- Secrets detection: Detects exposed keys, tokens, and credentials early, with custom patterns for organization-specific secrets.
- Unified governance: Applies consistent controls across developer and agentic contributions while centralizing findings for reporting and remediation.
SonarQube Remediation Agent
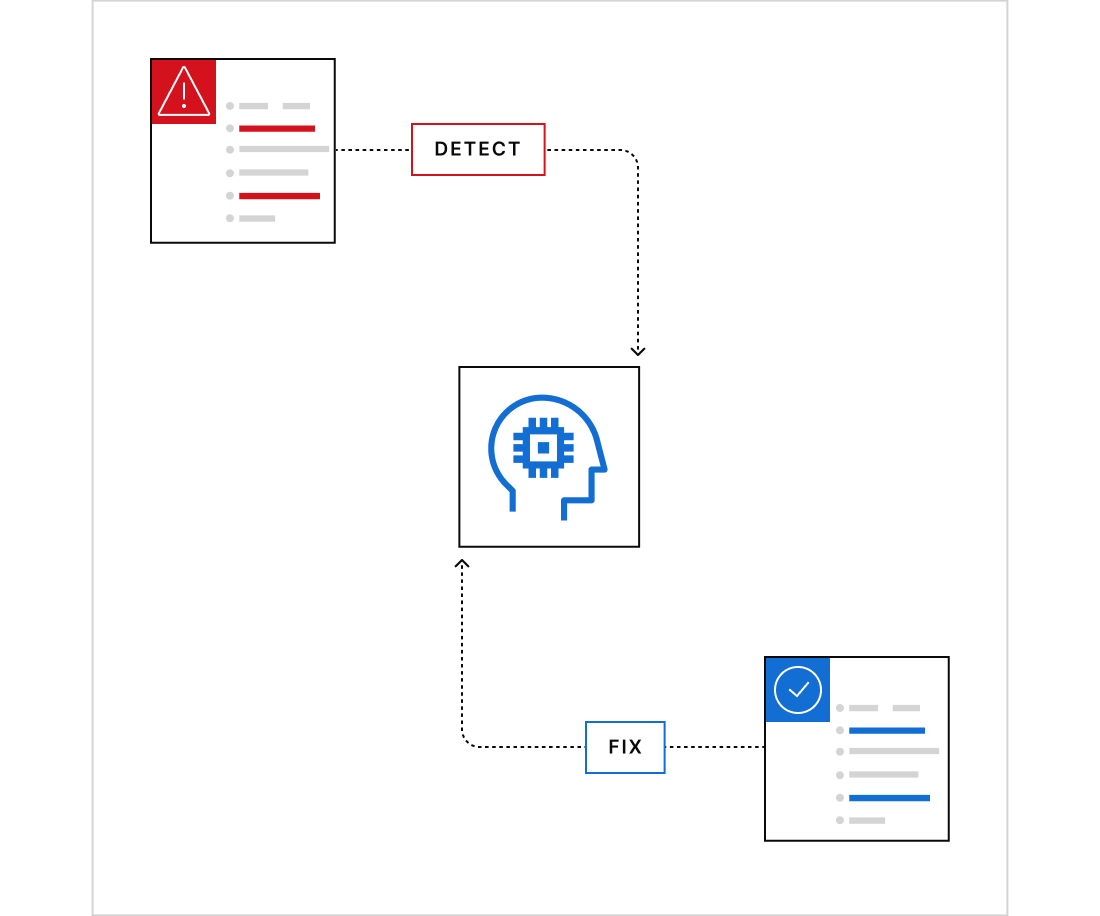
Scales remediation of findings and keeps fixes within established verification, review, and change control workflows.
- Accelerate remediation — Works through backlog findings asynchronously, reducing unresolved risk and helping teams restore release readiness faster.
- Verification before review — Reanalyzes proposed fixes with Sonar before opening a pull request, checking them against centralized standards.
- Sustained code health — Addresses security, reliability, and maintainability issues that might otherwise remain unresolved.
- Governed change delivery — Delivers fixes through pull requests, preserving human review and a clear history of each change.
SonarQube Hunter Agent
Extends compliance-relevant vulnerability discovery to complex access control, business logic, authentication, and session management flaws.
- Deeper vulnerability identification — Analyzes application behavior and workflows to uncover risks that conventional pattern-based scanning may not detect.
- Validated findings — Investigates potential issues before surfacing them, reducing noise and supporting focused risk triage.
- Centralized governance — Adds findings to the SonarQube issue workflow for consistent review, assignment, remediation tracking, and reporting.
Why choose SonarQube for regulatory compliance and reporting?
In-workflow compliance
We integrate compliance into the development lifecycle, making it a natural part of the process, not a separate phase.

Ease of reporting
Generate comprehensive evidence of compliance instantly, with a single click, simplifying your audit readiness and saving valuable time.

Actionable guidance
Get instant feedback on what steps need to be taken in order to close compliance gaps.
Resources
Full coverage of MISRA C++:2023
Read more
How SonarQube enables DORA compliance for financial institutions
Read more
Cyber Resilience Act: Navigating speed and security with AI-coding
Read more

What is SonarQube for compliance and reporting?
SonarQube for compliance and reporting helps organizations operationalize code compliance by setting centralized quality and security standards and enforcing them consistently across development workflows. Those standards are embedded into pull requests, CI/CD pipelines, and release processes, making them difficult to bypass and easier to apply at scale. SonarQube also provides transparent, centralized reporting that shows how policies are being enforced, where issues remain, and how remediation is progressing over time, helping teams support audit readiness, internal governance, and compliance reporting with clear evidence.
How does SonarQube help with code compliance?
SonarQube automates code review, applies centralized compliance rules, and reports issues directly in pull requests and branches. This helps teams catch non-compliant code before it is merged. It also creates a clear record of detection and remediation for audit purposes.
Which compliance standards does SonarQube support?
SonarQube supports a range of widely used security and coding standards, including OWASP Top 10, OWASP ASVS, PCI DSS, CWE Top 25, STIG, and MISRA C++:2023. It also helps organizations address code-related and secure development requirements in broader regulatory and policy frameworks such as the European Union Cyber Resilience Act (CRA), the Digital Operational Resilience Act (DORA), and NIST SSDF. With SonarQube Advanced Security, that support extends further into OSS and software supply chain risk through SCA, advanced SAST, license management, and SBOM generation.
Can SonarQube help with AI-generated code compliance?
Yes. SonarQube helps with AI-generated code compliance by applying the same centralized quality and security standards to AI-generated and human-written code, ensuring governance at the software delivery layer. SonarQube core capabilities support governance for teams using AI coding tools by embedding policy enforcement, review workflows, and reporting into everyday development. This helps organizations reduce the risk of non-compliant AI-assisted code entering production and gives compliance and security teams clearer evidence of how standards are being applied.
How does SonarQube simplify audit reporting?
SonarQube simplifies audit reporting by centralizing compliance evidence and making policy enforcement visible across everyday development workflows. It shows which quality and security standards are in place, where issues or policy breaches remain, and how remediation is progressing over time across pull requests, branches, and CI/CD pipelines. This gives teams a transparent record of enforcement and follow-up, reducing the manual effort needed to prepare for audits, support internal reviews, and produce compliance reporting.
How does SonarQube help with open source compliance risks?
SonarQube helps with open source compliance risks through Advanced Security and its SCA capabilities. It identifies vulnerabilities in third-party OSS dependencies, flags components that conflict with your organization’s license policies, and lets teams define license profiles with allowed and prohibited license rules across projects. It also supports SBOM export in SPDX and CycloneDX formats, giving organizations clearer visibility into OSS usage and stronger evidence for software supply chain governance and compliance reporting.