

Catch bugs and debt before they merge.
- Finds the issues that slow you down later. Reviews every branch and pull request for bugs, maintainability issues, and technical debt across 45+ languages.
- Gives the same answer every time. The same code gets the same findings, so results are explainable and repeatable for human and AI-written code.
- Keeps feedback inside your workflow. Findings show up in your IDE, agent session, and pull request, so nobody switches tools to see them.
- Moves from finding to fixing. AI CodeFix suggests a fix in the IDE or PR, and the Remediation Agent opens pull requests that are verified before you see them.
Find vulnerabilities while the code is still being written.
- Catches the vulnerabilities attackers use. SAST and taint analysis trace untrusted input across files and functions to find injection flaws, with fewer false positives.
- Stops leaked credentials before commit. Secrets detection flags API keys, tokens, and passwords in the IDE, commits, and pull requests.
- Covers mobile apps too. Android and iOS code is checked against the OWASP Mobile Top 10 before it reaches the app store.
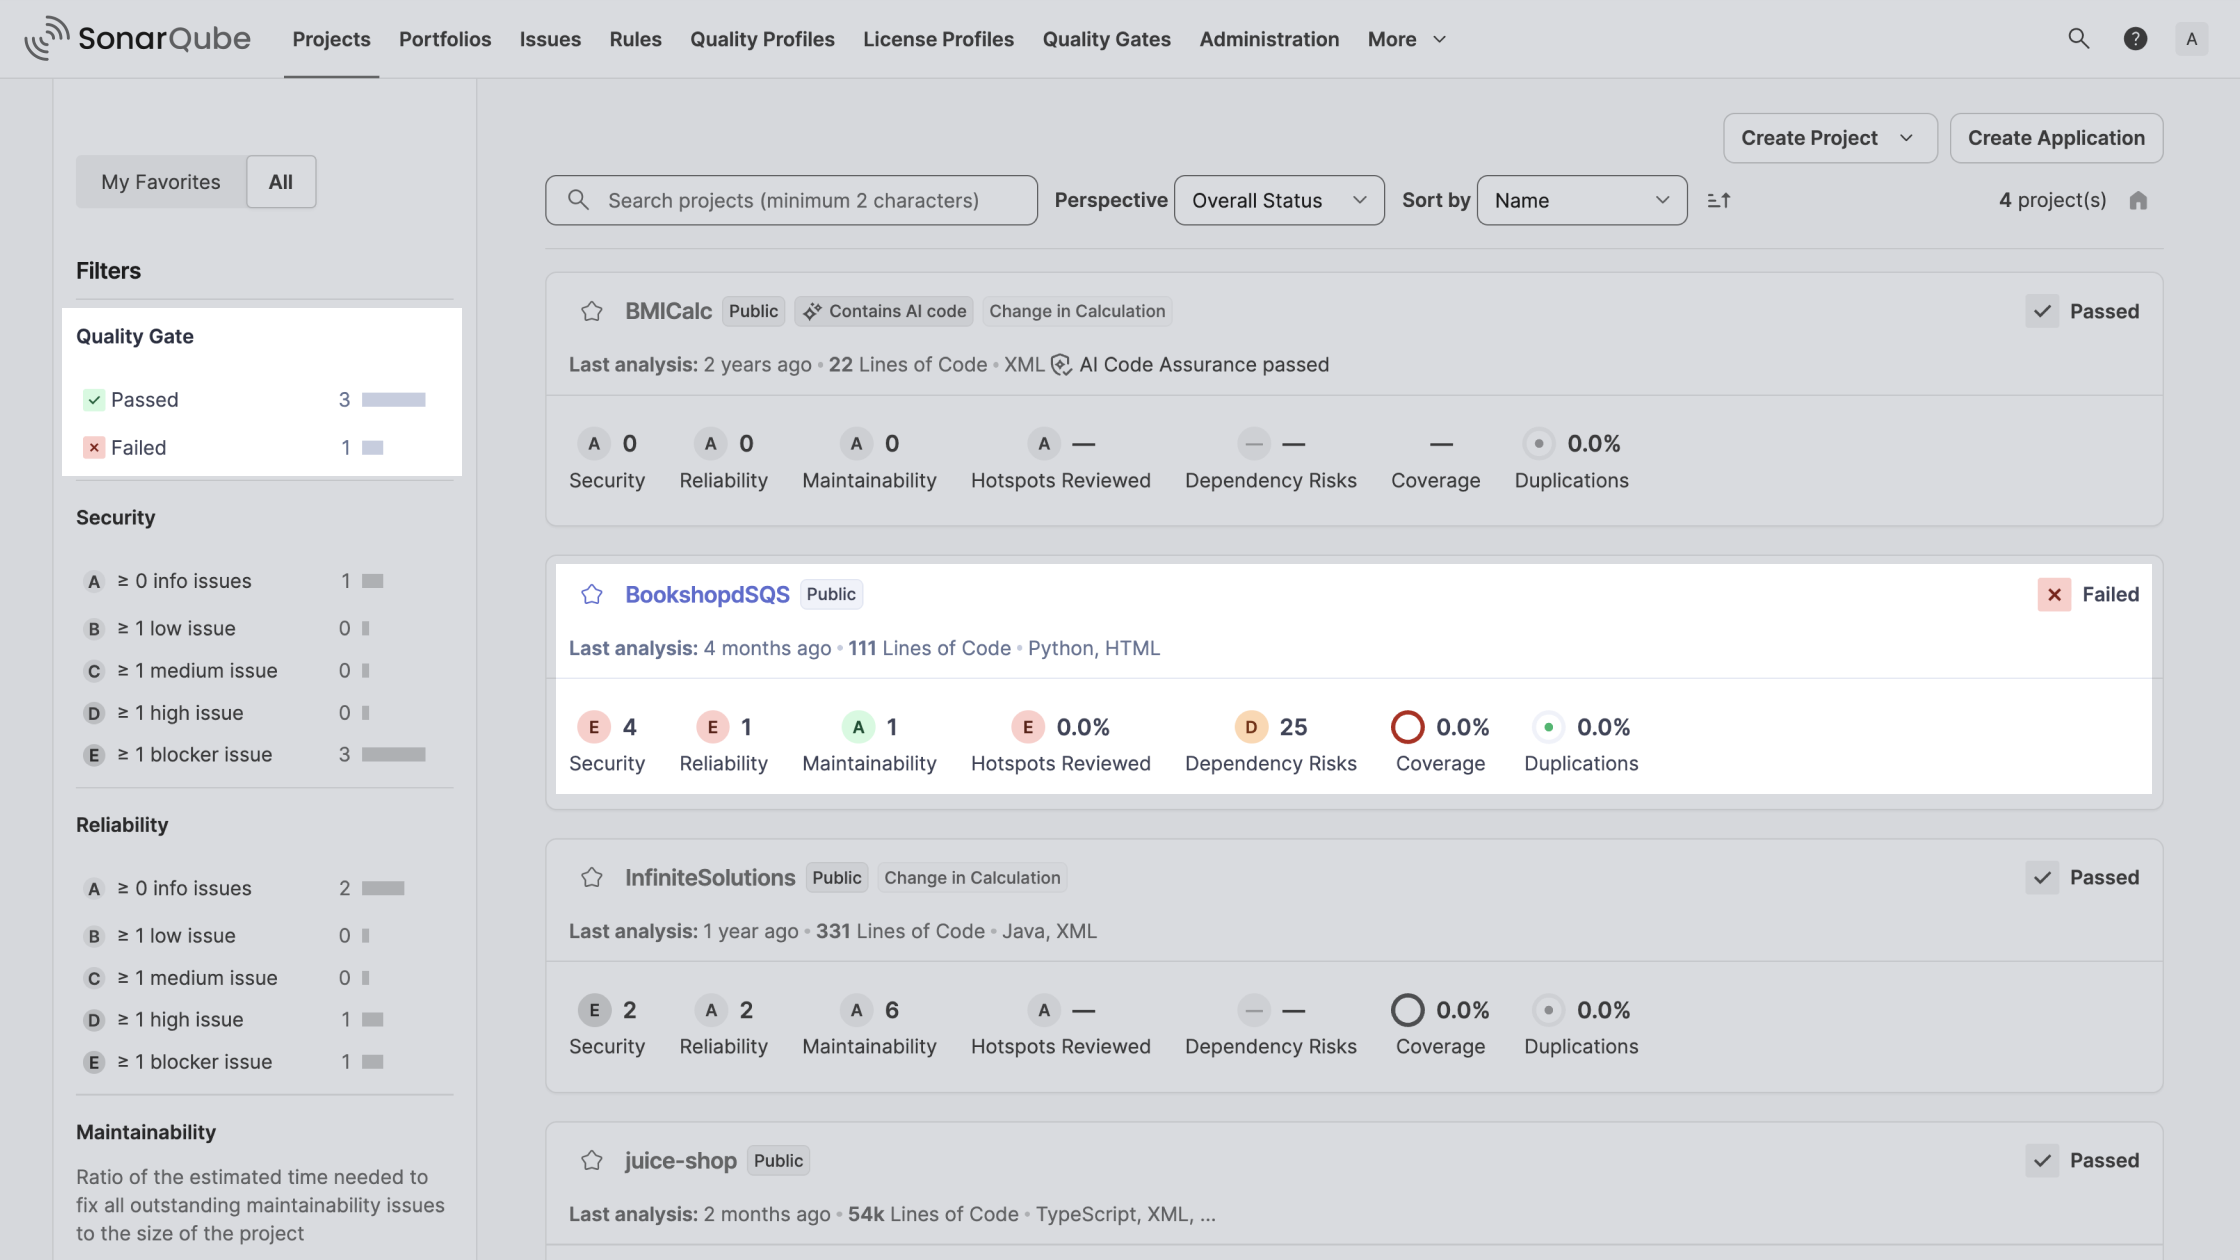
- Shows how secure you are. Security reports and a posture rating give leads one view across projects.
Know what's in your software, and what it exposes.
- Finds risky dependencies before they ship. SCA detects known vulnerabilities (CVEs) and malicious packages, with severity and exploit data to help you prioritize. Requires SonarQube Advanced Security.
- Proves what you ship. License checks run on every pull request, and a software bill of materials (SBOM) is ready for auditors.
- Catches cloud misconfigurations in review. IaC scanning checks Terraform, CloudFormation, Kubernetes, Docker, Helm, Ansible, and ARM for exposed services and insecure defaults.
Define your architecture. See where code drifts from it.
- Shows the architecture you actually have. SonarQube derives a living map from the code, with no diagramming by hand.
- Holds code to the design you intended. Architects define the intended structure, and deviations are flagged in your standard quality gates.
- Keeps AI-generated code in line. Humans and agents are checked against the same design, so a codebase stays modular as volume grows.
- Fixes drift in the workflow. Architectural issues are tracked and managed alongside every other finding.
Works where your team already works.
- In your agent session. Claude Code, Cursor, GitHub Copilot CLI, Devin, Windsurf, Gemini CLI, and Antigravity CLI.
- In your pull request. GitHub, GitLab, Bitbucket, and Azure DevOps show quality gate results right in the PR.
- In your pipeline. Jenkins, CircleCI, Harness, Maven, CodeMagic, and Amazon CodeCatalyst.
- In your editor. VS Code, Visual Studio, JetBrains IDEs, Eclipse, and Android Studio.
- In your wider toolchain. Jira, Slack, Datadog, JFrog, Docker Scout, and more.
Governance and reporting
- Governance and compliance: Provides centralized oversight and reporting necessary to enforce regulatory standards and corporate security policies across your organization.
- Security reports: See where you stand against OWASP Top 10, OWASP Mobile Top 10, CWE Top 25, OWASP ASVS, OWASP MASVS, OWASP Top 10 for LLM Applications, PCI DSS, STIG ASD, and CASA, then download them as a PDF. Available starting in Enterprise Edition.
- Project and portfolio management: High-level visibility and aggregated data across all projects, allowing leaders to monitor risk, track compliance, and ensure coding standards.
- Reporting and analytics: Provides actionable insights and automated reports to monitor trends, evaluate risk, and drive data-backed decisions across the organization.