Find deeply hidden security issues
99% of software applications use and interact with the code in third-party libraries (dependencies). Deeper SAST from Sonar extends code analysis and scanning to cover the unknown parts of the code that are in the open-source dependencies. Scanning dependencies (libraries) allows Sonar SAST to extend the dataflow analysis and find deeply hidden security issues in code that other tools cannot find. Deeper SAST is available today for Java, C#, and JavaScript/TypeScript in SonarQube Server and SonarQube Cloud.

Accelerate secure development
SAST analysis of Pull Requests helps empower developers by shifting security left and presenting security vulnerabilities as early as possible in the process - when the code is fresh in mind and the fix is still easy. SAST is available by default with SonarQube Server and SonarQube Cloud and runs as part of a normal code analysis and integrates seamlessly with the DevSecOps pipeline.

Reduce risk of security breaches
By implementing secure code development practices to strengthen the quality of the codebase, organizations can prevent malicious actors from exploiting vulnerabilities and stealing sensitive information. Sonar analyzers raise issues (including bugs and vulnerabilities) and security hotspots as it scans the code to detect security problems. Cloud secrets detection capabilities extend to include more rules that discover unintended hard-coded passwords, credentials, tokens, cloud access keys, API keys, cloud account/keys in the most popular cloud providers: AWS, GCP, Microsoft Azure, IBM, and Alibaba Cloud.

Automate code scanning
Sonar SAST can scan large amounts of code quickly – saving time and money in the software development life cycle process. Automating code scanning with SAST helps improve the overall security posture of an application and reduces the reliance on manual code reviews, allowing developers to focus on remediation efforts while maintaining an efficient and secure development lifecycle.
Code Security and compliance
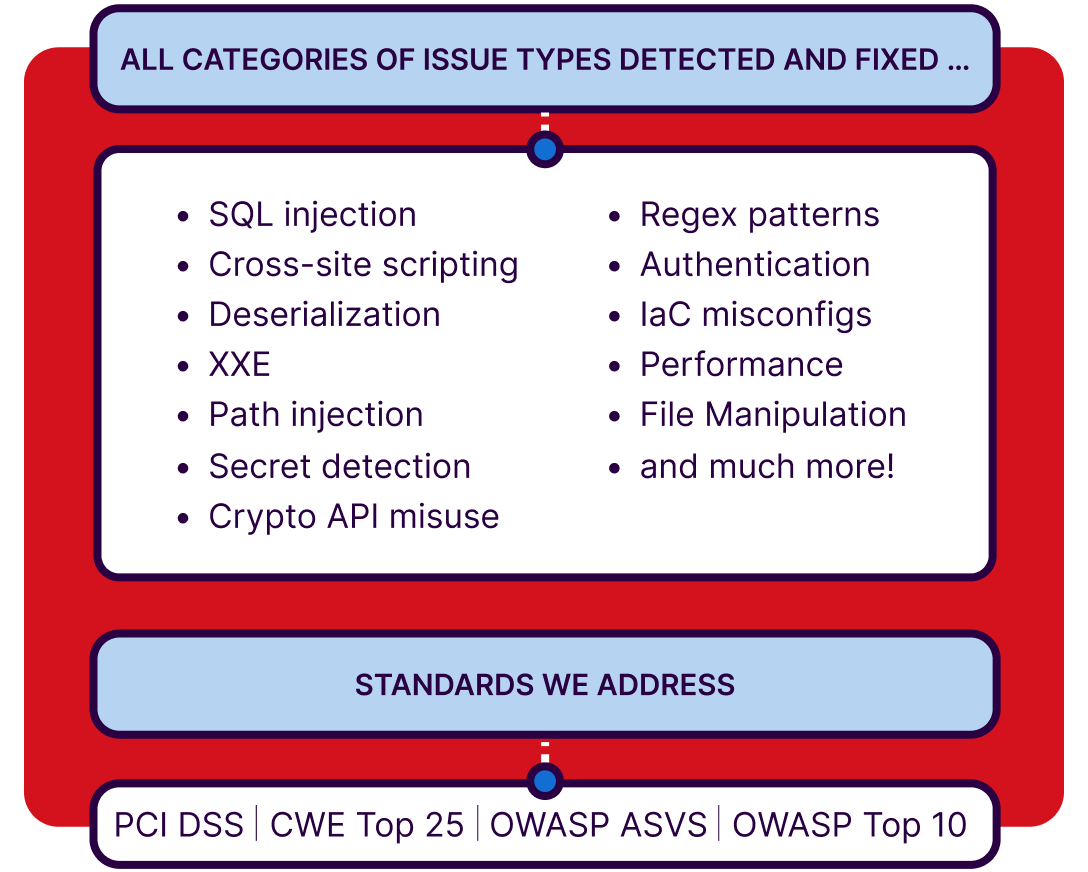
Sonar provides comprehensive application security tracking and governance for the most complex projects with SAST. Dedicated reports track the application’s code security against standards such as OWASP Top 10, OWASP ASVS, CWE Top 25 (2021, 2020, and 2019), as well as PCI DSS.

Comprehensive Detection Engine and coverage
Sonar provides code quality and security analysis for 30+ languages (and frameworks), with more than 5,100 out-of-the-box Code Quality rules. Sonar detects bugs and security flaws at the code level – source code, support code (including config code, infrastructure code, scripting, and test code), and third-party code, such as external dependencies and libraries – often exceeding a true positive rate (TPR) of 90%. Security coverage includes cross-site scripting, SQL injection, path injection, to secrets, IaC misconfigurations, phishing, and a variety of others.